Social Engineering
Recognizing Social Engineering: Common Methods and Defenses
Not every cyber attack starts with malware. Many begin with a phone call, a friendly email, or a person waiting politely at the office door. Social engineering targets people rather than technical vulnerabilities, and that is exactly why it works so well. This article looks at the methods attackers use, the warning signs that give them away and how teams can protect themselves.
What is social engineering?
Social engineering refers to attacks in which criminals deliberately exploit human behavior: helpfulness, respect for authority, time pressure, or simply everyday routine. Instead of breaking through firewalls, attackers persuade employees to disclose information, approve payments, or open doors. Technical safeguards only go so far here. What counts is that your team knows the tricks and reacts correctly.
The most common methods
Pretexting: The attacker invents a credible pretext and poses as IT support, a supplier, a government official, or a new colleague. These stories are often enriched with details researched beforehand on the company website or social networks. The more plausible the pretext, the lower the suspicion.
Phishing and spear phishing: Fake emails ask recipients to click links, open attachments, or enter credentials. While classic phishing is sent out broadly, spear phishing targets specific individuals or departments and appears especially credible thanks to personal details.
Vishing: In voice phishing, attackers call directly: as a supposed bank employee, as the "IT department" with an urgent security issue, or as a manager who needs a payment processed immediately. The pressure of a live conversation leaves many people little time to think.
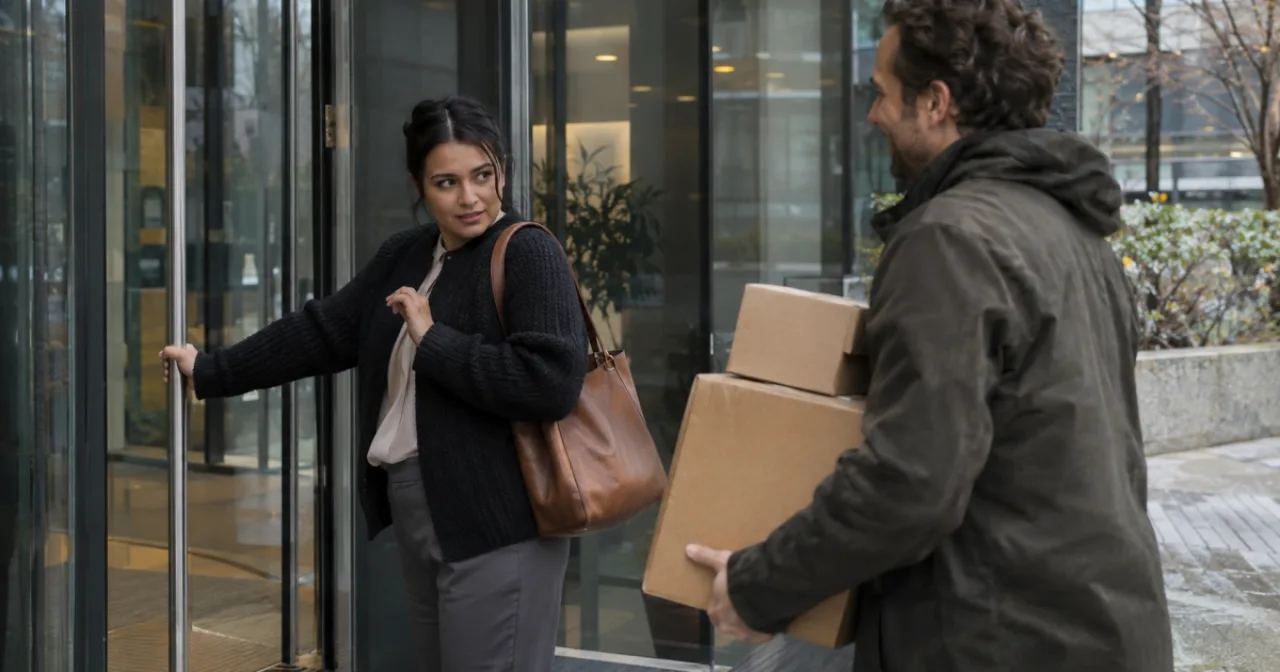
Tailgating: Here, attackers gain physical access by simply following authorized staff through secured doors, often with their hands full, carrying parcels, or dressed as tradespeople, so that someone politely holds the door open.
QR scams (quishing): Manipulated QR codes on posters, invoices, or in emails lead to fake login pages or trigger downloads unnoticed. Because hardly anyone checks the destination URL when scanning, QR scams bypass many familiar precautions.
Typical warning signs
However different the methods are, the patterns behind them are similar. Watch out for these signals:
- Urgency and time pressure: "immediately", "today", "before your account is locked".
- Unusual requests from familiar senders: sudden payment instructions, gift card purchases, or requests for credentials.
- Appeals to secrecy: "Please don't discuss this with anyone."
- Details that don't add up: slightly altered sender addresses, unknown callback numbers, links that don't match the supposed organization.
- Emotional triggers: fear, curiosity, or helpfulness deliberately played upon.
Rules of conduct for teams
These warning signs translate into simple, effective rules:
- Verify identity via a second channel: For unusual requests, call back on a known number, never using the contact details from the suspicious message.
- Never share credentials: Legitimate IT departments and banks do not ask for passwords, by phone or by email.
- Check links and QR codes before opening: Look at the destination URL. When in doubt, type the address manually.
- Don't grant access out of politeness: Kindly direct unknown visitors to reception instead of holding doors open.
- Report suspicious incidents immediately: An open, blame-free culture is essential. Anyone who has clicked one link too many must be able to report it without fear. Every early report protects the whole company.
Why training and simulation make the difference
A one-off briefing is not enough, because social engineering tactics change constantly. What works is the combination of regular training and realistic practice: courses teach the methods and rules of conduct, while simulations turn them into lived routine. Anyone who has already encountered a deceptively genuine phishing email in a safe environment recognizes the real thing much faster.
For many organizations, this is no longer optional: the NIS2 directive, in force in Austria since 1 October 2026, requires affected organizations to implement cyber hygiene measures and corresponding training, among other things. Find out what this means in practice on our NIS2 page.
With Protectly, you combine both: hands-on security awareness training and realistic phishing simulations that prepare your team specifically for social engineering attacks. See for yourself and book a demo.
This is exactly what Protectly trains: book a free demo.